
Industrial IoT security protocols: where compatibility creates risk
Publication Date
author
As connected factories expand, industrial IoT security protocols are becoming a hidden fault line between efficiency and exposure. For quality-control teams and security managers, the real challenge is not only choosing secure standards, but understanding how protocol compatibility across devices, gateways, and legacy systems can quietly introduce risk. This article examines where interoperability strengthens operations—and where it creates dangerous blind spots.
Why compatibility has become the new risk signal in industrial environments
A few years ago, many plant security discussions focused on perimeter defense, network segmentation, and patching. Those controls still matter, but the operating context has changed. Industrial networks now connect PLCs, sensors, machine vision devices, gateways, MES platforms, remote maintenance tools, and cloud analytics layers that were once isolated. In that shift, industrial IoT security protocols are no longer selected in clean, single-vendor environments. They are deployed across mixed fleets, retrofit lines, and edge architectures where compatibility often takes priority over security design.
This is the trend that quality-control personnel and security managers need to track: the more organizations push for data continuity, predictive maintenance, and cross-site visibility, the more they depend on protocol bridges, converters, and shared interfaces. Those compatibility layers can improve uptime and accelerate integration, yet they can also weaken authentication, reduce encryption consistency, and create asset visibility gaps. In practice, risk is not always introduced by a “bad” protocol alone. It often appears when a relatively secure protocol is forced to coexist with a weaker legacy standard, a rushed gateway configuration, or a vendor implementation that supports only partial security features.
The market shift: from isolated control networks to interoperable data pipelines
The strongest signal in the market is not simply that more devices are online. It is that more industrial decisions now depend on data moving across system boundaries. Quality teams want traceability from sensor to batch record. Maintenance teams want alerts from machines delivered into enterprise dashboards. Procurement teams want equipment that can integrate quickly with existing OT and IT systems. Executives want scalable architectures rather than closed islands of automation.
That demand is reshaping how industrial IoT security protocols are evaluated. In the past, protocol selection could be driven by machine compatibility and deterministic performance. Today, buyers increasingly ask whether the protocol stack supports secure onboarding, role-based access, certificate handling, encrypted transport, logging, and lifecycle management across multiple vendors. The difficulty is that compatibility pressures often push in the opposite direction. Plants need equipment that “just works” with Modbus, OPC UA, MQTT, PROFINET, EtherNet/IP, BACnet, serial-to-IP converters, and custom middleware all at once.
The result is a new risk profile: interoperability has become a business requirement, but unmanaged interoperability has become a security liability.
Why industrial IoT security protocols are under more pressure than before
Several forces are driving this change. First, modernization is happening unevenly. A facility may have a new vision inspection station with modern encryption support next to older controllers that still rely on weak or nonexistent native security. Second, procurement priorities have broadened. Buyers are no longer selecting only for throughput, tolerance, and cycle time; they also need data interoperability, software support, and security maintainability. Third, compliance expectations are rising. Even where regulations differ by sector and geography, audit pressure around asset inventory, access control, traceability, and incident readiness is increasing.
For TSV’s audience, the most important insight is that protocol risk now affects product quality and operational reliability, not just cybersecurity posture. If a protocol bridge silently drops messages, allows stale data, or creates ambiguous timestamps, the problem becomes a quality issue. If a weak compatibility setting enables unauthorized parameter changes, it becomes both a safety and process integrity issue. This is why industrial IoT security protocols should be assessed as part of engineering assurance, not only IT policy.
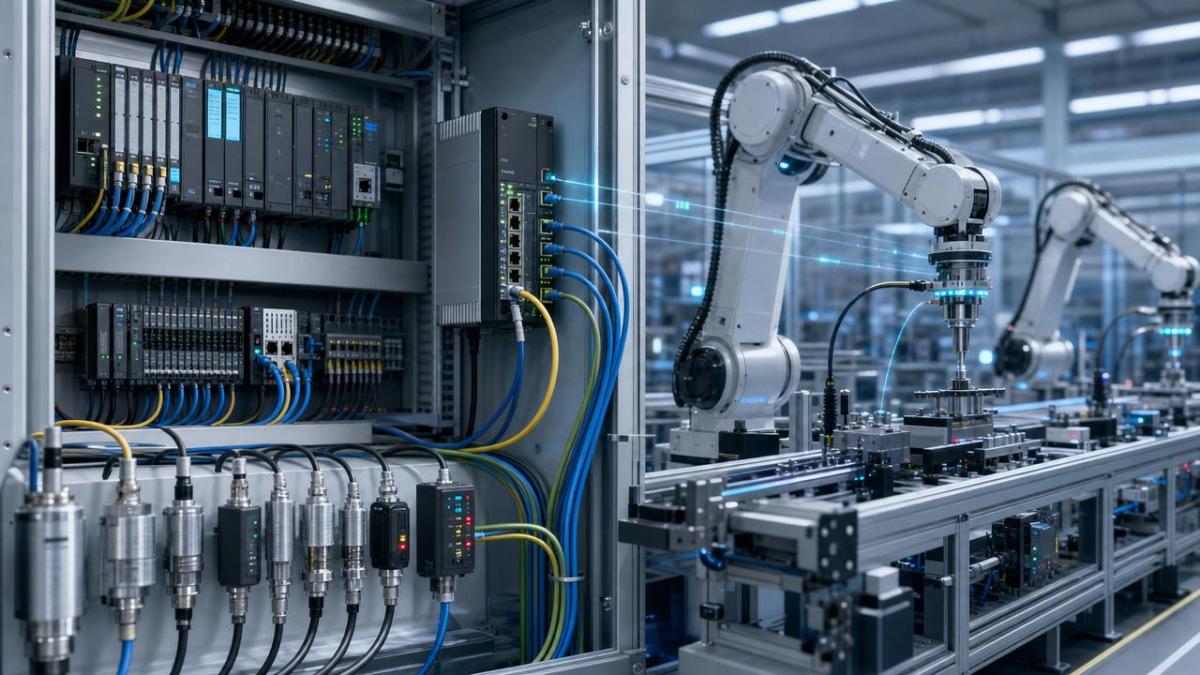
Where interoperability strengthens operations—and where it turns into a blind spot
Interoperability is not the problem by itself. In many cases, it is essential. Standardized data exchange can improve OEE analysis, support digital quality records, and reduce manual inspection delays. Secure protocol adoption can also improve monitoring fidelity and make anomaly detection more practical. The risk appears when compatibility is treated as a shortcut instead of an engineered control layer.
Common blind spots include protocol downgrades, where a secure system communicates through a less secure intermediary for the sake of compatibility. Another is feature mismatch: a protocol may support encryption and authentication in theory, but a device implementation may ship with those functions disabled, unsupported, or too difficult to maintain at scale. A third blind spot is ownership ambiguity. OT teams may manage line uptime, IT teams may manage certificates, and vendors may manage remote support channels. When responsibility is split, industrial IoT security protocols can look compliant on paper while remaining fragile in operation.
Security managers should also watch for “invisible exposure.” These are paths created by engineering laptops, temporary diagnostic services, unmanaged serial converters, or firmware constraints that are rarely documented in quality plans. Compatibility projects often happen under production pressure, which means temporary exceptions can become permanent architecture.
The impact on quality-control teams and security managers is becoming more direct
For quality-control personnel, the protocol layer is increasingly relevant because data trust is now part of quality assurance. If inspection devices, environmental sensors, or inline metrology systems send data through insecure or unstable pathways, calibration confidence and traceability can be compromised. A quality deviation may no longer come from a machine defect alone; it may come from delayed, altered, or incomplete data exchange.
For security managers, the challenge is broader than blocking attacks. They must evaluate whether industrial IoT security protocols are implemented consistently across vendors, whether asset discovery includes protocol translators and edge nodes, and whether incident response plans cover OT-specific communication failures. In many plants, the highest risk is not a dramatic ransomware headline scenario. It is a lower-profile event: unauthorized access to a control parameter, an unverified firmware update path, or a protocol bridge that bypasses standard logging.
A practical trend to monitor: protocol support is becoming a procurement differentiator
One of the clearest shifts in the industrial market is that protocol support is no longer a simple checkbox. Buyers increasingly distinguish between nominal compatibility and secure compatibility. A vendor may claim support for modern industrial IoT security protocols, but decision-makers should ask deeper questions. Does the implementation support certificate rotation without line disruption? Can access rights be segmented by role? Are logs exportable for OT incident review? Is secure mode enabled by default, or only available through custom engineering effort?
This matters because procurement decisions lock in risk for years. In sectors with long equipment lifecycles, a weak protocol implementation becomes a persistent operational burden. For mixed-industry manufacturers, the ability to compare vendors through hard technical criteria—not marketing language—is becoming essential. This is exactly where a data-driven engineering approach adds value: compatibility should be measured in terms of security behavior, integration friction, and lifecycle support, not only connection success.
How to judge whether compatibility is creating risk in your plant
A useful judgment framework starts with three questions. First, where are secure protocols being translated into less secure forms? Second, which devices or gateways act as trust concentrators across multiple lines or sites? Third, which protocol paths affect quality records, alarm logic, or parameter control? These questions help separate theoretical exposure from business-critical exposure.
Security managers should map protocol dependencies the same way reliability teams map failure points. Quality teams should identify data streams that influence release decisions, traceability, or compliance evidence. If those streams depend on undocumented bridges, shared credentials, or unsupported firmware, risk is already present. Industrial IoT security protocols should also be reviewed during change management, especially when adding sensors, remote access features, or cloud dashboards that appear operationally harmless.
The next phase: secure-by-design interoperability rather than retrofit security
The long-term direction is becoming clearer across advanced manufacturing: interoperability will remain non-negotiable, but tolerance for insecure compatibility will continue to shrink. As plants adopt more edge AI, distributed sensing, and cross-facility benchmarking, protocol decisions will increasingly influence audit readiness, supplier qualification, and resilience planning. The organizations that adapt fastest will not be those with the most tools, but those that treat protocol architecture as an engineering control with measurable requirements.
That means moving away from reactive bolt-ons. Instead of asking how to secure a compatibility layer after deployment, leading teams ask earlier whether the intended industrial IoT security protocols align with asset criticality, support lifecycle governance, and preserve data integrity under real operating conditions. In other words, they evaluate the protocol path the way they evaluate tolerances, failure modes, and process capability.
Action priorities for the next review cycle
For organizations deciding what to do next, the most effective response is not to replace every legacy asset at once. It is to improve visibility and discipline around compatibility risk. Start by ranking communication paths according to operational consequence. Review where industrial IoT security protocols intersect with quality-critical data, remote maintenance, and line-control authority. Require vendors to document not only supported protocols but supported security modes, default settings, and update practices. Treat gateways, converters, and middleware as critical assets rather than neutral accessories.
Finally, align OT, IT, quality, and procurement around one shared standard of evidence. If a protocol claim cannot be validated through configuration detail, support documentation, and operational testing, it should not be accepted as low risk. For enterprises trying to judge how this trend affects their own operations, the key questions are straightforward: Which compatibility layers do we depend on most? Which of them influence product quality or safety? Which vendors can demonstrate secure interoperability in measurable terms? Those answers will shape not just cybersecurity outcomes, but the trustworthiness of the modern connected factory itself.
Search News
Hot Articles
- Carbon Fiber StructuresHow to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsJul 11, 2026
- Machine VisionXiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsMar 30, 2026
- Cobots & ArmsShanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsMar 30, 2026
Popular Tags
Recommended News
 Jul 11, 2026How to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsAerospace carbon fiber assemblies: learn how to specify laminate design, load data, joining methods, and inspection controls for lighter, reliable load-bearing aerospace parts.Elena Rostova (UAV Systems Researcher)
 Mar 30, 2026Xiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsXiaomi & Alibaba DAMO Academy's open-source robotics models lower algorithm barriers for global SMEs. Boost efficiency in manufacturing, logistics & smart retail with ROS 2 compatible solutions.TSV Data Lab
 Mar 30, 2026Shanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsShanxi 'AI+' Conference highlights embodied intelligence with Tesla, Ubtech & Jiantao showcasing multimodal robotics. 40+ global buyers validated tech on-site, creating new B2B channels for industrial automation & AI solutions.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Zhongguancun Unveils 6G Integrated Sensing-Computing-Intelligence Platform to Empower Embodied Robots for Global Industrial ApplicationsZhongguancun's new 6G platform revolutionizes industrial robotics with <10ms latency, empowering global automotive, logistics & port automation. Discover how this tech boosts China's smart manufacturing exports.TSV Data Lab
 Mar 30, 2026Mech-Mind Tianjin Embodied Intelligence R&D and Production Base Goes Live, Cutting Delivery Time by 20%–30% for Global Customized AMR+Vision SolutionsMech-Mind's Tianjin AMR+Vision production base cuts delivery time by 20%-30% for欧美 & Latin American markets. Discover how this PLd-certified facility accelerates customized robotics solutions for smart manufacturing and logistics.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Boao Forum Reveals 'Co-evolution of Big and Small Brains' Trend in Humanoid Robots, China's Embodied Intelligence Accelerates Adaptation to Overseas Manufacturing Service ScenariosDiscover how China's humanoid robots, featuring 'Co-evolution of Big and Small Brains,' are revolutionizing global manufacturing. Learn about Embodied Tian Gong 3.0's ISO compliance and overseas deployment at Boao Forum 2026.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026China Railway Industrial Secures Patent for Embodied Robotics in Material Handling, Boosting High-Precision Delivery Capabilities for Overseas Infrastructure and Manufacturing ProjectsChina Railway Industrial's new patent for embodied robotics in material handling boosts high-precision delivery for global infrastructure & manufacturing. Discover how this innovation enhances logistics accuracy in automotive, rail transit & EPC projects.Chen Wei (Automation Lead Engineer)
 Sep 28, 2026Spindle Runout Measurement in Germany: DIN Standards, Methods, and Acceptance LimitsSpindle runout measurement Germany: explore DIN standards, proven methods, acceptance limits, and audit-ready practices for reliable machining quality.Dr. Marcus Vance
 Sep 27, 2026How to Select Wall-Mount Edge Devices for Space-Constrained Factory NetworksWall mount edge devices for space-constrained factories: evaluate workload, thermal design, power resilience, cable access, and network reliability for smarter deployments.TSV Data Lab
 Sep 26, 2026Machining Tolerance Analysis: How to Set Limits That Meet Function and Cost TargetsMachining tolerance analysis: learn how to set functional limits, control tolerance stacks, reduce inspection risk, and balance precision with production cost.Dr. Marcus Vance
 Sep 25, 2026How to Evaluate an Industrial Infrastructure Data Platform for Multi-Site OperationsIndustrial infrastructure data platform evaluation guide for multi-site operations: compare data quality, edge resilience, interoperability, governance, and scalable proof-of-value criteria.Victor Lin (Chief Software Architect)
 Sep 24, 2026How to Select Machine Vision Optics for Accurate Inspection at Different Working DistancesMachine vision optics selection guide for accurate inspection at every working distance. Compare FOV, pixel scale, DOF, distortion, lighting, and telecentric options.TSV Data Lab
 Sep 23, 2026How to Evaluate a Machine Vision System Integrator for High-Speed Inspection LinesChoose a machine vision system integrator with proven expertise in high-speed inspection, reliable reject timing, robust optics, and measurable acceptance criteria.TSV Data Lab
 Sep 28, 2026When is a SCADA API the right choice for connecting plant systems?SCADA API guide: learn when governed plant data integration improves traceability, security, and scalability—without compromising real-time control.Victor Lin (Chief Software Architect)
 Sep 27, 2026How SCADA data integration improves traceability across production linesSCADA data integration connects production-line data to improve traceability, accelerate quality investigations, and strengthen safety decisions.Victor Lin (Chief Software Architect)
 Sep 26, 2026What to define before starting SCADA integration planningSCADA integration planning starts with clear scope, control boundaries, data models, cybersecurity, and testing. Discover the definitions that reduce risk and costly rework.Victor Lin (Chief Software Architect)
 Sep 25, 2026How a smart factory with Industrial IoT reduces production blind spotsDiscover how a smart factory with Industrial IoT turns real-time machine, quality, and workflow data into actionable insights that reduce production blind spots and delivery risks.Victor Lin (Chief Software Architect)
 Sep 24, 2026When does Industrial IoT make smart manufacturing easier to scale?Smart manufacturing Industrial IoT scales when trusted data, interoperable systems, and secure workflows turn connected assets into measurable gains.TSV Data Lab
 Sep 23, 2026What drives ultra-precision machining cost at 1-micron tolerance?Ultra precision machining cost per part at 1 micron tolerance depends on process, material, metrology, and yield. Learn how to compare quotes confidently.Dr. Marcus Vance
 Sep 22, 2026Drone Engine-T550CC Applications: Build the UAV Power System Around the MissionAn application guide for Drone Engine-T550CC integration, covering payload planning, airframe matching, cooling, fuel, vibration, test procedures, documentation, and service preparation.Elena Rostova (UAV Systems Researcher)
 Sep 22, 2026How to Evaluate Industrial Edge Computing Vendors for Factory DeploymentIndustrial edge computing vendor evaluation guide for factories: compare latency, protocol fit, reliability, security, and lifecycle support before deployment.TSV Data Lab
 Sep 21, 2026Drone Payload Integration: Matching Power, Data, and Center of Gravity for Reliable FlightsDrone payload integration made practical: balance power, data, center of gravity, and endurance to build safer, more reliable mission-ready flights.Elena Rostova (UAV Systems Researcher)
 Sep 20, 2026Autonomous Navigation Pricing: Cost Drivers and Budget Benchmarks for AMR ProjectsAutonomous navigation price explained: compare AMR cost drivers, software, sensors, integration, safety, and lifecycle budgets to build a scalable project plan.Chen Wei (Automation Lead Engineer)
 Sep 19, 2026How to Scope Automation Integration Services for Multi-System Factory ProjectsAutomation integration services: learn how to scope multi-system factory projects with clear workflows, interface contracts, safety boundaries, and acceptance criteria.Victor Lin (Chief Software Architect)























