
Collaborative robots safety standards are changing system design
Publication Date
author
Collaborative robots safety standards are reshaping how engineers, quality teams, and safety managers approach system architecture, risk assessment, and compliance validation. As cobots move deeper into high-mix, precision manufacturing, outdated design assumptions can expose operations to performance gaps and regulatory risk. This article examines how evolving safety requirements are changing system design priorities—and what decision-makers must verify before deployment.
For quality control teams and safety managers, the issue is no longer whether a cobot can share space with people. The real question is whether the complete system—robot arm, end effector, sensors, software, guarding logic, and operating procedure—meets current expectations for safe, repeatable production. In many facilities, a deployment that looked acceptable 3 to 5 years ago may now require a more detailed risk assessment, clearer validation records, and tighter control of speed, force, stopping performance, and operator interaction zones.
At TechStat Vanguard, the practical concern is straightforward: marketing language does not protect a line from an incident, a failed audit, or an expensive redesign. Parameters do. For buyers and compliance reviewers, collaborative robots safety standards now influence layout decisions, payload selection, tool design, commissioning steps, and even supplier qualification timelines that typically range from 4 to 12 weeks.
Why collaborative robot safety standards now affect system design earlier
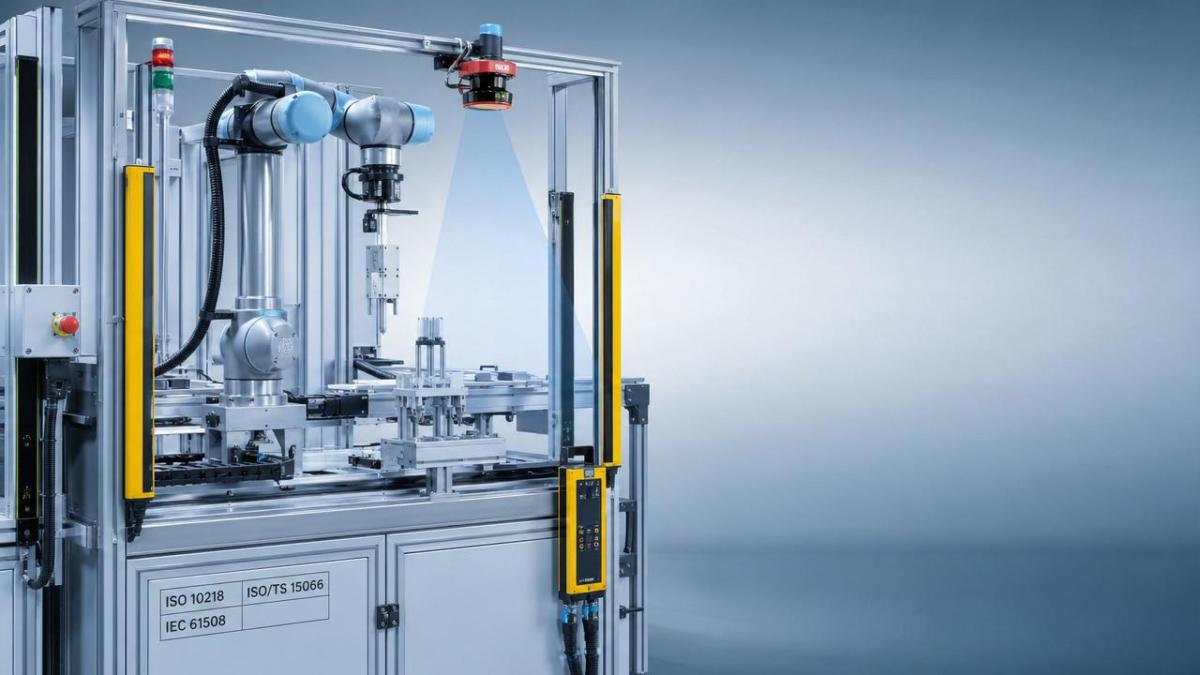
A cobot used to be evaluated mainly as a machine component. Today, it is reviewed as part of an integrated application. That shift matters because collaborative robots safety standards increasingly focus on actual operating conditions: contact risk, stopping response, pinch points, tool geometry, part presentation, and human behavior during reset, cleaning, loading, and maintenance.
In practice, this means safety cannot be added at the end of the project. If risk reduction is delayed until factory acceptance testing, teams often discover that the intended cycle time, reach envelope, or end-of-arm tooling creates unacceptable exposure. A line designed for 12 parts per minute may drop to 8 or 9 parts per minute if speed and separation controls were not considered from the start.
From robot selection to application validation
Modern procurement reviews should separate four layers of analysis: robot capability, application hazard profile, environmental conditions, and validation evidence. A 10 kg payload cobot with 1300 mm reach may be suitable for machine tending, but the same unit can become high risk when fitted with a sharp gripper, handling hot parts above 60°C, or working beside two operators in a narrow aisle less than 1.2 meters wide.
- Robot body limitations: payload, reach, repeatability, joint speed, stopping distance
- Tooling factors: pinch edges, clamping force, vacuum loss, sharp corners, part retention
- Workspace factors: aisle width, access points, maintenance access, nearby manual stations
- Control factors: reset logic, mode selection, safety I/O, scanner zones, fault recovery steps
Standards are changing what “safe by design” means
For many buyers, “safe by design” once meant relying on the robot’s built-in collaborative features. That is no longer enough. Collaborative robots safety standards push teams to verify the whole application, not only the arm. Built-in functions such as speed monitoring, power and force limiting, and emergency stop behavior still matter, but they must be matched with task-specific controls and documented acceptance criteria.
This is especially important in precision manufacturing, electronics assembly, aerospace subassembly, and medical device machining support, where contact tolerances may be tight, parts may be fragile, and operator interaction may occur dozens of times per shift. In such environments, even a small mismatch—such as a gripper closing force 15% above target or an unvalidated restart sequence—can create safety and quality issues at the same time.
Common triggers for redesign
- End effectors added late without force or pinch-point review
- Scanner zones set too conservatively, reducing throughput by 10% to 25%
- Insufficient evidence of stopping performance under full payload conditions
- Manual recovery tasks not included in the original risk assessment
- Operator training limited to normal production mode, excluding fault handling
The table below shows how design assumptions are changing as collaborative robots safety standards mature across industrial environments.
The key conclusion is simple: compliance is moving upstream. When collaborative robots safety standards are addressed only during final approval, companies often pay twice—once for installation, and again for redesign, retesting, and delayed production release.
What quality and safety teams should verify before deployment
Before approving a cobot cell, quality and safety teams should verify not just whether documents exist, but whether they describe the real process. A strong review normally covers at least 6 areas: application boundaries, hazard identification, control architecture, operating limits, validation testing, and lifecycle management. Missing just 1 of these areas can weaken the entire approval package.
1. Define the actual collaborative mode
Not all cobot tasks operate the same way. Some applications rely on monitored stop when a person enters the cell. Others use hand-guiding, speed and separation monitoring, or power and force limiting. Safety managers should confirm which mode is active during each production step, including loading, unloading, clearing jams, and maintenance. One line may use 2 or 3 different collaborative behaviors across a single shift.
2. Review force, speed, and contact assumptions
If the application depends on power and force limiting, the review cannot stop at brochure claims. Teams should verify how speed limits were established, how contact risk was evaluated, and whether end-of-arm tooling changes the exposure profile. A blunt gripper and a narrow metal finger do not create the same risk, even at the same robot speed. The same is true when payload changes from 2 kg to 6 kg.
Minimum validation questions
- What is the maximum programmed speed in each zone?
- What is the stopping response under full payload and worst-case reach?
- What is the gripper closing force or vacuum retention margin?
- Are there sharp edges, hot surfaces, or trapped part risks?
- How often are tool wear and sensor drift checked—daily, weekly, or per shift?
3. Validate abnormal conditions, not only normal production
A common weakness in cobot projects is that qualification focuses on steady-state operation for 20 or 30 minutes, while real production includes stoppages, mispicks, restarts, and operator interventions. For quality control personnel, the most useful approval evidence often comes from abnormal-case testing: sensor loss, dropped parts, incomplete clamp closure, communication delay, emergency stop recovery, and manual jog authorization.
A practical validation protocol may include 15 to 30 test cases, depending on complexity. High-mix environments with frequent SKU changes may require version-controlled recipes, lockable parameter sets, and revalidation after tooling replacement. If product changeovers happen 3 to 8 times per week, configuration discipline becomes a safety issue, not just a quality issue.
The checklist below helps teams translate collaborative robots safety standards into a usable pre-deployment review framework.
The strongest deployments treat this checklist as a release gate. If one item is incomplete, production start should be delayed. That discipline may add 2 to 5 days in commissioning, but it can prevent months of corrective action later.
How evolving standards change procurement, layout, and supplier evaluation
For procurement leaders and plant engineers, collaborative robots safety standards now shape vendor selection as much as payload or price. Two suppliers may offer similar reach, repeatability, and list cost, yet differ sharply in safety documentation quality, test support, tooling integration discipline, and change-control capability. Those differences directly affect approval speed and lifecycle risk.
Procurement criteria should go beyond hardware specs
A useful supplier evaluation model includes at least 5 dimensions: technical fit, safety evidence, integration support, maintainability, and traceability of changes. For example, if a vendor can provide clear safety function descriptions, commissioning test templates, and documented parameter backup procedures, the qualification cycle may be reduced from 10 weeks to 6 or 7 weeks in a well-prepared project.
- Ask for application-specific risk review support, not generic brochures.
- Check whether tooling and robot controls are validated as one system.
- Confirm spare part strategy for sensors, grippers, cables, and safety devices.
- Require revision tracking for software, recipes, and safety parameter changes.
- Review service response expectations, such as 24-hour remote support or 72-hour onsite windows.
Layout decisions are becoming more data-driven
In older projects, teams often tried to maximize openness around the cobot cell. Today, the better approach is to map human movement patterns, intervention frequency, and part flow with more discipline. If operators enter the workspace 40 times per shift, the design should account for approach direction, visibility, and stop-zone behavior from the beginning. If maintenance access is only needed once every 2 weeks, that zone can be treated differently.
This approach helps avoid the false choice between safety and productivity. In many cells, productivity loss comes not from stricter safety expectations, but from poor layout logic. A scanner field that is too broad, a tray position that forces cross-body reach, or a reset button placed outside the operator’s natural line of sight can all add friction without reducing actual risk.
Typical design trade-offs to evaluate
- Open access versus selective guarding for low-frequency service areas
- Higher robot speed versus longer protective distance
- Compact footprint versus maintenance clearance of 600 to 900 mm
- Faster gripper action versus lower pinch-force exposure
For facilities managing regulated quality systems or customer audits, these design choices should be documented in a form that connects layout, risk controls, and validation outcomes. That record becomes valuable when a line is duplicated across 2, 5, or 10 sites, or when a customer requests process traceability before supplier approval.
Practical implementation roadmap for safer cobot deployment
A practical rollout does not start with the robot. It starts with a structured application review. For most manufacturers, a 4-step process is more effective than trying to solve safety during installation week. This is particularly true in sectors where uptime targets exceed 85% to 90%, and unplanned redesign can disrupt multiple production schedules.
Step 1: Map the task and operator interaction
Document part weight, shape, temperature, edge condition, takt time, and all operator touchpoints. Include routine interactions such as replenishment every 20 minutes, quality checks every 1 hour, and jam recovery once per shift if that is typical. This prevents underestimating exposure.
Step 2: Build the safety concept with tooling and controls together
Do not approve the arm first and the end effector later. The gripper, vacuum circuit, part presentation, and sensing architecture should be reviewed as a single system. If the tool changes, the risk profile may change. If the payload increases by 30%, stopping and contact assumptions may also need review.
Step 3: Validate normal and abnormal cases
Commissioning should include not only production runs, but restart logic, fault recovery, operator intervention, and loss-of-signal scenarios. Record pass/fail criteria and corrective actions. A disciplined 1-day validation event can reveal issues that would otherwise remain hidden for months.
Step 4: Control the lifecycle after launch
Post-launch discipline is essential. Changes to grippers, product variants, speed settings, scanner zones, or software versions should trigger review rules. Even a small unauthorized adjustment can invalidate the original safety assumptions. For plants with frequent engineering changes, a monthly review cycle is often more realistic than annual-only checks.
Collaborative robots safety standards are not only a compliance topic. They are now a design, procurement, and operational control topic. For quality personnel, they help reduce hidden variation in deployment quality. For safety managers, they create a stronger basis for approval and incident prevention. For engineering and sourcing teams, they provide a clearer filter for selecting capable integration partners.
TechStat Vanguard supports decision-makers who need evidence rather than marketing claims: measurable application boundaries, realistic validation logic, and traceable technical benchmarks. If you are evaluating a cobot project, updating a supplier qualification process, or reviewing an existing line against current expectations, now is the right time to tighten the engineering data behind your decision. Contact us to discuss your application, request a tailored evaluation framework, or learn more solutions for safer, more reliable collaborative automation.
Search News
Hot Articles
- Carbon Fiber StructuresHow to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsJul 11, 2026
- Machine VisionXiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsMar 30, 2026
- Cobots & ArmsShanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsMar 30, 2026
Popular Tags
Recommended News
 Jul 11, 2026How to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsAerospace carbon fiber assemblies: learn how to specify laminate design, load data, joining methods, and inspection controls for lighter, reliable load-bearing aerospace parts.Elena Rostova (UAV Systems Researcher)
 Mar 30, 2026Xiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsXiaomi & Alibaba DAMO Academy's open-source robotics models lower algorithm barriers for global SMEs. Boost efficiency in manufacturing, logistics & smart retail with ROS 2 compatible solutions.TSV Data Lab
 Mar 30, 2026Shanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsShanxi 'AI+' Conference highlights embodied intelligence with Tesla, Ubtech & Jiantao showcasing multimodal robotics. 40+ global buyers validated tech on-site, creating new B2B channels for industrial automation & AI solutions.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Zhongguancun Unveils 6G Integrated Sensing-Computing-Intelligence Platform to Empower Embodied Robots for Global Industrial ApplicationsZhongguancun's new 6G platform revolutionizes industrial robotics with <10ms latency, empowering global automotive, logistics & port automation. Discover how this tech boosts China's smart manufacturing exports.TSV Data Lab
 Mar 30, 2026Mech-Mind Tianjin Embodied Intelligence R&D and Production Base Goes Live, Cutting Delivery Time by 20%–30% for Global Customized AMR+Vision SolutionsMech-Mind's Tianjin AMR+Vision production base cuts delivery time by 20%-30% for欧美 & Latin American markets. Discover how this PLd-certified facility accelerates customized robotics solutions for smart manufacturing and logistics.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Boao Forum Reveals 'Co-evolution of Big and Small Brains' Trend in Humanoid Robots, China's Embodied Intelligence Accelerates Adaptation to Overseas Manufacturing Service ScenariosDiscover how China's humanoid robots, featuring 'Co-evolution of Big and Small Brains,' are revolutionizing global manufacturing. Learn about Embodied Tian Gong 3.0's ISO compliance and overseas deployment at Boao Forum 2026.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026China Railway Industrial Secures Patent for Embodied Robotics in Material Handling, Boosting High-Precision Delivery Capabilities for Overseas Infrastructure and Manufacturing ProjectsChina Railway Industrial's new patent for embodied robotics in material handling boosts high-precision delivery for global infrastructure & manufacturing. Discover how this innovation enhances logistics accuracy in automotive, rail transit & EPC projects.Chen Wei (Automation Lead Engineer)
 Sep 28, 2026Spindle Runout Measurement in Germany: DIN Standards, Methods, and Acceptance LimitsSpindle runout measurement Germany: explore DIN standards, proven methods, acceptance limits, and audit-ready practices for reliable machining quality.Dr. Marcus Vance
 Sep 27, 2026How to Select Wall-Mount Edge Devices for Space-Constrained Factory NetworksWall mount edge devices for space-constrained factories: evaluate workload, thermal design, power resilience, cable access, and network reliability for smarter deployments.TSV Data Lab
 Sep 26, 2026Machining Tolerance Analysis: How to Set Limits That Meet Function and Cost TargetsMachining tolerance analysis: learn how to set functional limits, control tolerance stacks, reduce inspection risk, and balance precision with production cost.Dr. Marcus Vance
 Sep 25, 2026How to Evaluate an Industrial Infrastructure Data Platform for Multi-Site OperationsIndustrial infrastructure data platform evaluation guide for multi-site operations: compare data quality, edge resilience, interoperability, governance, and scalable proof-of-value criteria.Victor Lin (Chief Software Architect)
 Sep 24, 2026How to Select Machine Vision Optics for Accurate Inspection at Different Working DistancesMachine vision optics selection guide for accurate inspection at every working distance. Compare FOV, pixel scale, DOF, distortion, lighting, and telecentric options.TSV Data Lab
 Sep 23, 2026How to Evaluate a Machine Vision System Integrator for High-Speed Inspection LinesChoose a machine vision system integrator with proven expertise in high-speed inspection, reliable reject timing, robust optics, and measurable acceptance criteria.TSV Data Lab
 Sep 28, 2026When is a SCADA API the right choice for connecting plant systems?SCADA API guide: learn when governed plant data integration improves traceability, security, and scalability—without compromising real-time control.Victor Lin (Chief Software Architect)
 Sep 27, 2026How SCADA data integration improves traceability across production linesSCADA data integration connects production-line data to improve traceability, accelerate quality investigations, and strengthen safety decisions.Victor Lin (Chief Software Architect)
 Sep 26, 2026What to define before starting SCADA integration planningSCADA integration planning starts with clear scope, control boundaries, data models, cybersecurity, and testing. Discover the definitions that reduce risk and costly rework.Victor Lin (Chief Software Architect)
 Sep 25, 2026How a smart factory with Industrial IoT reduces production blind spotsDiscover how a smart factory with Industrial IoT turns real-time machine, quality, and workflow data into actionable insights that reduce production blind spots and delivery risks.Victor Lin (Chief Software Architect)
 Sep 24, 2026When does Industrial IoT make smart manufacturing easier to scale?Smart manufacturing Industrial IoT scales when trusted data, interoperable systems, and secure workflows turn connected assets into measurable gains.TSV Data Lab
 Sep 23, 2026What drives ultra-precision machining cost at 1-micron tolerance?Ultra precision machining cost per part at 1 micron tolerance depends on process, material, metrology, and yield. Learn how to compare quotes confidently.Dr. Marcus Vance
 Sep 22, 2026Drone Engine-T550CC Applications: Build the UAV Power System Around the MissionAn application guide for Drone Engine-T550CC integration, covering payload planning, airframe matching, cooling, fuel, vibration, test procedures, documentation, and service preparation.Elena Rostova (UAV Systems Researcher)
 Sep 22, 2026How to Evaluate Industrial Edge Computing Vendors for Factory DeploymentIndustrial edge computing vendor evaluation guide for factories: compare latency, protocol fit, reliability, security, and lifecycle support before deployment.TSV Data Lab
 Sep 21, 2026Drone Payload Integration: Matching Power, Data, and Center of Gravity for Reliable FlightsDrone payload integration made practical: balance power, data, center of gravity, and endurance to build safer, more reliable mission-ready flights.Elena Rostova (UAV Systems Researcher)
 Sep 20, 2026Autonomous Navigation Pricing: Cost Drivers and Budget Benchmarks for AMR ProjectsAutonomous navigation price explained: compare AMR cost drivers, software, sensors, integration, safety, and lifecycle budgets to build a scalable project plan.Chen Wei (Automation Lead Engineer)
 Sep 19, 2026How to Scope Automation Integration Services for Multi-System Factory ProjectsAutomation integration services: learn how to scope multi-system factory projects with clear workflows, interface contracts, safety boundaries, and acceptance criteria.Victor Lin (Chief Software Architect)























