Robot Safety Systems for Robot Cells: How to Choose Guards, Sensors, and PLC Safety Logic
Publication Date
author
Choosing robot safety systems for robot cells is less about passing an audit and more about proving that risk has been reduced by design. In automated production, the real question is not whether guards, sensors, and safety PLC logic are present, but whether they match the robot’s speed, reach, payload, stopping distance, and human interaction pattern.
That is why robot safety systems for robot cells deserve closer attention across general industry. As lines become denser, faster, and more connected, weak safety architecture can create hidden downtime, unsafe bypass behavior, and expensive redesigns after commissioning.
From a TechStat Vanguard perspective, engineering truth starts with measurable parameters. Safety performance should be judged through verifiable distances, diagnostic coverage, fault response, and reset logic rather than broad vendor claims.
What a robot cell safety system really includes
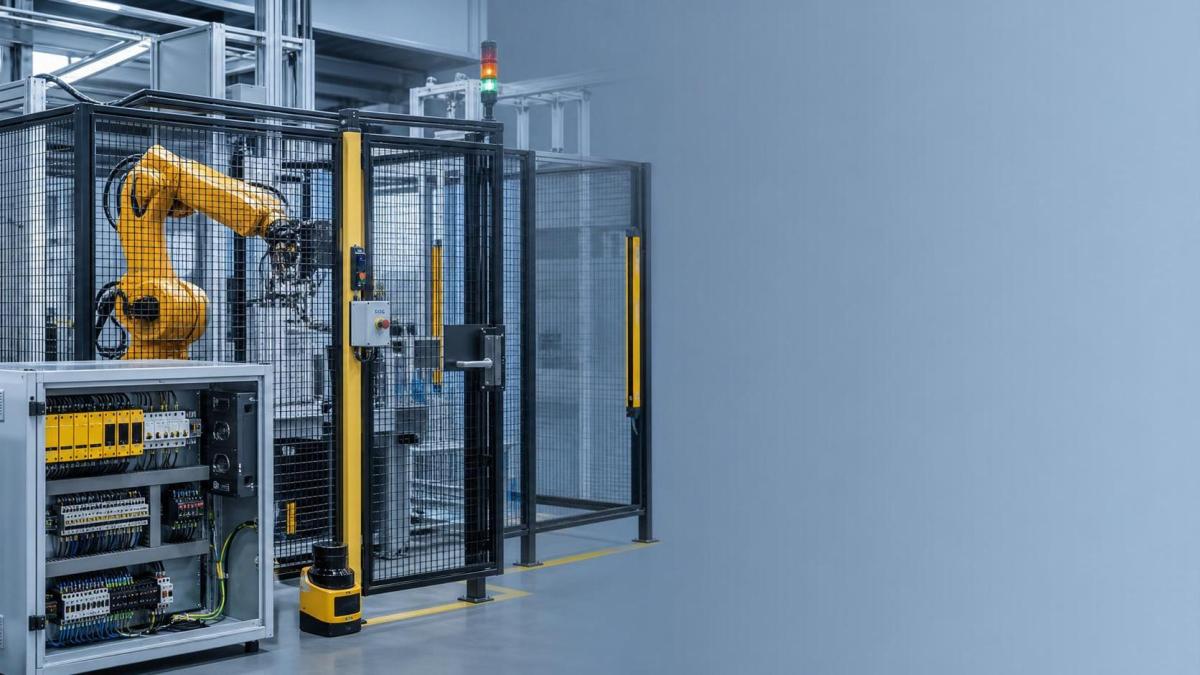
A robot cell safety system is a layered control structure. It usually combines physical separation, presence detection, safe motion control, operator access management, and logic that forces the machine into a defined safe state.
In practical terms, robot safety systems for robot cells often include fixed fencing, interlocked doors, area scanners, light curtains, safety mats, emergency stops, enabling devices, and a safety-rated PLC or relay architecture.
The point of layering is simple. One component should not carry the entire risk burden. If a sensor is misaligned or an access point is opened, another layer should still limit exposure.
This matters even more in mixed-process cells. Welding, machine tending, palletizing, adhesive dispensing, inspection, and collaborative handling all create different hazard profiles, even when the same robot model is used.
Why selection has become harder
Robot cells are no longer isolated cages with one clear entry point. Modern layouts often include conveyors, AGV interfaces, vision systems, manual load zones, maintenance access, and remote diagnostics.
As a result, choosing robot safety systems for robot cells now requires more than checking a catalog. Safety devices must be evaluated against process variability, software states, restart conditions, and foreseeable operator behavior.
Another challenge is market noise. Many products are presented as complete solutions, while the critical details remain unclear: response time, muting logic limits, contamination sensitivity, fault exclusion assumptions, or integration constraints with the robot controller.
In TSV’s data-first view, vague claims should never replace system-level analysis. A high-spec sensor does not guarantee a safe cell if stopping time, mounting height, and access geometry were poorly defined.
Start with the hazard, not the device list
A good selection process begins with the robot’s actual risk envelope. That means mapping motion range, tool hazards, pinch points, end-effector failure modes, and areas where people may enter during normal production or service.
The most useful questions are operational. How often is access required? Is intervention planned or exceptional? Does the robot stop safely under load? Can stored energy remain after the servo stop?
Standards such as ISO 10218, ISO 13849, IEC 62061, and ISO 13855 provide the framework, but the application detail drives the final architecture. Two cells can share the same standard and still need different protections.
How to choose guards and physical barriers
Physical guarding remains the most stable layer in many robot cells. Fixed fencing is still the right answer where access is infrequent and robot speed or payload makes presence sensing alone insufficient.
The key is geometry, not just material strength. Fence height, ground clearance, opening size, and setback distance must prevent reach-over, reach-under, and reach-through access to the hazard zone.
Interlocked gates should be selected according to the stopping behavior of the cell. If the hazard persists after the guard is opened, guard locking may be required rather than a simple interlock.
In high-throughput environments, poor gate placement can create repeat interference with production flow. That often leads to improvised shortcuts, which is a strong indicator that the original safety concept ignored real operations.
Where fixed guards work best
- Cells with predictable motion and limited manual interaction
- Applications with hot, sharp, or ejecting process hazards
- Installations where contamination could impair optical sensors
- Layouts requiring strong separation during maintenance or recovery
When sensors add value, and when they do not
Presence sensing can improve access efficiency, but only when the sensing field matches the hazard and the machine can achieve a safe stop in time. This is where many robot safety systems for robot cells are either well engineered or fundamentally weak.
Light curtains are effective at controlled openings with clear ingress paths. Safety laser scanners are useful for irregular zones, corner protection, and warning-to-stop strategies in dynamic areas.
Safety mats can help at defined standing positions, though they are less flexible in harsh environments and layout changes. Interlock switches remain essential where the act of opening a door must trigger the safety function.
What matters most is response chain timing. Sensor reaction time, PLC logic time, network latency where relevant, actuator delay, and robot stopping time all affect the required safety distance.
Useful sensor selection checks
- Confirm the protective field cannot be stepped around or reached over
- Verify resistance to dust, smoke, glare, coolant, and vibration
- Check restart interlock logic after field interruption
- Review muting or blanking only where justified and documented
- Measure actual stop time during commissioning, not just design time
Why PLC safety logic deserves equal scrutiny
Hardware selection gets attention because it is visible. Safety logic is less visible, yet it determines whether devices interact in a controlled and diagnosable way. Weak logic can undermine otherwise capable components.
A safety PLC should clearly define input status, safe outputs, reset conditions, fault handling, and mode selection. Automatic restart after interruption is often a major concern unless the risk assessment explicitly supports it.
For robot safety systems for robot cells, the logic often needs to coordinate safe torque off, safe speed monitoring, safe limited position, gate monitoring, muting conditions, and emergency stop zones.
The better approach is transparent cause-and-effect mapping. Every triggered device should produce a predictable state change, a clear fault indication, and a controlled recovery path.
Logic issues worth catching early
- Reset permitted while a person remains inside the protected zone
- Shared signals that hide which device actually caused the stop
- Mode changes without adequate key control or supervision
- Maintenance overrides lacking timeout, indication, or authorization
- No proof test strategy for critical safety channels
Typical cell types need different safety architectures
A palletizing cell often favors fenced separation with interlocked access because movements are repetitive and payloads are large. A machine-tending cell may need guarded loading zones with light curtains or scanner-based access control.
Welding cells usually require strong attention to spatter, fumes, arc flash isolation, and sensor contamination. Assembly cells with human intervention may rely more on safe speed, enabling devices, and carefully managed teach modes.
This is why copying a previous design can be risky. Even minor process changes can alter the best combination of guards, sensors, and PLC safety logic.
A practical decision path
For most facilities, the strongest next step is to build a parameter-based review instead of a product-first shortlist. Start with measured stop time, real access points, intervention frequency, and environmental stressors.
Then compare whether fixed guards, sensor-based access, or mixed protection gives the most credible reduction in risk without encouraging bypass behavior. After that, verify the safety PLC sequence against actual operating modes, not a simplified diagram.
In the TSV framework, robot safety systems for robot cells should be judged the same way as any critical hard-tech decision: by traceable assumptions, measured performance, and documented limits. That creates a more reliable basis for specification, supplier comparison, and long-term change control.
A well-chosen safety architecture does more than protect people. It reduces false trips, shortens validation debates, and makes future modifications easier to assess with confidence. The next review should focus on where exposure really occurs, which parameters are proven, and which claims still need engineering evidence.
Search News
Hot Articles
- Carbon Fiber StructuresHow to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsJul 11, 2026
- Machine VisionXiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsMar 30, 2026
- Cobots & ArmsShanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsMar 30, 2026
Popular Tags
Recommended News
 Jul 11, 2026How to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsAerospace carbon fiber assemblies: learn how to specify laminate design, load data, joining methods, and inspection controls for lighter, reliable load-bearing aerospace parts.Elena Rostova (UAV Systems Researcher)
 Mar 30, 2026Xiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsXiaomi & Alibaba DAMO Academy's open-source robotics models lower algorithm barriers for global SMEs. Boost efficiency in manufacturing, logistics & smart retail with ROS 2 compatible solutions.TSV Data Lab
 Mar 30, 2026Shanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsShanxi 'AI+' Conference highlights embodied intelligence with Tesla, Ubtech & Jiantao showcasing multimodal robotics. 40+ global buyers validated tech on-site, creating new B2B channels for industrial automation & AI solutions.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Zhongguancun Unveils 6G Integrated Sensing-Computing-Intelligence Platform to Empower Embodied Robots for Global Industrial ApplicationsZhongguancun's new 6G platform revolutionizes industrial robotics with <10ms latency, empowering global automotive, logistics & port automation. Discover how this tech boosts China's smart manufacturing exports.TSV Data Lab
 Mar 30, 2026Mech-Mind Tianjin Embodied Intelligence R&D and Production Base Goes Live, Cutting Delivery Time by 20%–30% for Global Customized AMR+Vision SolutionsMech-Mind's Tianjin AMR+Vision production base cuts delivery time by 20%-30% for欧美 & Latin American markets. Discover how this PLd-certified facility accelerates customized robotics solutions for smart manufacturing and logistics.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Boao Forum Reveals 'Co-evolution of Big and Small Brains' Trend in Humanoid Robots, China's Embodied Intelligence Accelerates Adaptation to Overseas Manufacturing Service ScenariosDiscover how China's humanoid robots, featuring 'Co-evolution of Big and Small Brains,' are revolutionizing global manufacturing. Learn about Embodied Tian Gong 3.0's ISO compliance and overseas deployment at Boao Forum 2026.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026China Railway Industrial Secures Patent for Embodied Robotics in Material Handling, Boosting High-Precision Delivery Capabilities for Overseas Infrastructure and Manufacturing ProjectsChina Railway Industrial's new patent for embodied robotics in material handling boosts high-precision delivery for global infrastructure & manufacturing. Discover how this innovation enhances logistics accuracy in automotive, rail transit & EPC projects.Chen Wei (Automation Lead Engineer)
 Oct 04, 2026CAD/CAM Benchmarking in the GCC: What Manufacturers Should Ask a ConsultantCAD CAM benchmark consultant GCC guide: learn the key questions manufacturers should ask to validate post-processors, workflows, machine performance, and production risk.Victor Lin (Chief Software Architect)
 Oct 03, 2026Selecting Automotive Radar Sensor Modules for ADAS Range, Resolution, and IntegrationAutomotive radar sensor module selection guide for ADAS: compare range, resolution, field of view, latency, and integration to build safer, reliable vehicle systems.TSV Data Lab
 Oct 02, 2026How to Qualify Machined Parts Suppliers for Hard Tech ProgramsHard tech supply chain machined parts demand rigorous supplier qualification. Learn how to assess capability, traceability, quality controls, and delivery resilience.Dr. Marcus Vance
 Oct 01, 2026How to Select an Outdoor Security Radar Sensor for Perimeter Detection?Outdoor security radar sensor selection guide: compare range, accuracy, false-alarm control, integration, and field testing for reliable perimeter detection.TSV Data Lab
 Sep 30, 2026How to Evaluate Solid-State LiDAR Hardware for Outdoor Autonomous VehiclesSolid state LiDAR hardware evaluation guide for outdoor autonomous vehicles—compare range, point-cloud quality, environmental resilience, integration, and safety.TSV Data Lab
 Sep 29, 2026ISO 9283 Repeatability: How to Evaluate Cobot Positioning PerformanceISO 9283 cobot repeatability explained: learn how payload, reach, approach direction, and test conditions affect positioning performance and cell capability.Chen Wei (Automation Lead Engineer)
 Oct 04, 2026How Should You Compare 5-Axis CNC Machine Accuracy Claims?How do I compare 5-axis CNC machine accuracy claims? Learn how to assess standards, thermal stability, TCP accuracy, and real-world test evidence.Dr. Marcus Vance
 Oct 03, 2026Is Edge Computing Necessary for Real-Time Quality Inspection?Is industrial edge computing necessary for real-time quality inspection? Explore how latency, data volume, reliability, and control integration shape the right architecture.TSV Data Lab
 Oct 02, 2026What Documents Prove a Precision Machining Supplier Can Hold Tolerance?What documents prove a precision machining supplier can hold tolerance? Explore certificates, FAI reports, calibration, SPC, and traceability evidence to qualify suppliers with confidence.Dr. Marcus Vance
 Oct 01, 2026Can a Machining Supplier Meet Aerospace Fatigue Testing Requirements?Can a machining supplier meet aerospace fatigue testing requirements? Learn the traceability, process control, and test evidence needed for reliable aerospace parts.Dr. Marcus Vance
 Sep 30, 2026Which Industrial Robot Specifications Matter for High-Precision Assembly?Which industrial robot specifications matter most for high-precision assembly? Explore repeatability, accuracy, stiffness, vibration, calibration, and force control for reliable yields.Chen Wei (Automation Lead Engineer)
 Sep 29, 2026How Do You Verify Servo Motor Torque Under Continuous Load?How do I verify servo motor torque under continuous load? Learn RMS torque checks, torque-speed limits, thermal derating, and real-machine testing.Chen Wei (Automation Lead Engineer)
 Oct 02, 2026ZD330 Software Configuration: Verifying Cut-List Import Before PurchaseZD330 software and machine configuration: verify cut-list imports, data mapping, labels, and workflow before purchase to reduce errors and choose with confidence.Victor Lin (Chief Software Architect)
 Sep 28, 2026Spindle Runout Measurement in Germany: DIN Standards, Methods, and Acceptance LimitsSpindle runout measurement Germany: explore DIN standards, proven methods, acceptance limits, and audit-ready practices for reliable machining quality.Dr. Marcus Vance
 Sep 27, 2026How to Select Wall-Mount Edge Devices for Space-Constrained Factory NetworksWall mount edge devices for space-constrained factories: evaluate workload, thermal design, power resilience, cable access, and network reliability for smarter deployments.TSV Data Lab
 Sep 26, 2026Machining Tolerance Analysis: How to Set Limits That Meet Function and Cost TargetsMachining tolerance analysis: learn how to set functional limits, control tolerance stacks, reduce inspection risk, and balance precision with production cost.Dr. Marcus Vance
 Sep 25, 2026How to Evaluate an Industrial Infrastructure Data Platform for Multi-Site OperationsIndustrial infrastructure data platform evaluation guide for multi-site operations: compare data quality, edge resilience, interoperability, governance, and scalable proof-of-value criteria.Victor Lin (Chief Software Architect)