
When should a scada system integrator be replaced?
Publication Date
author
A failing scada system integrator rarely announces itself with a single catastrophic error.
Warning signs usually appear as slower deployments, unclear documentation, rising downtime, poor cybersecurity discipline, and weak alignment with production KPIs.
The real question is whether the scada system integrator still protects continuity, data integrity, and long-term scalability.
Replacement should be judged through engineering evidence, not vendor loyalty, habit, or polished commercial claims.
Operational Role of a Scada System Integrator
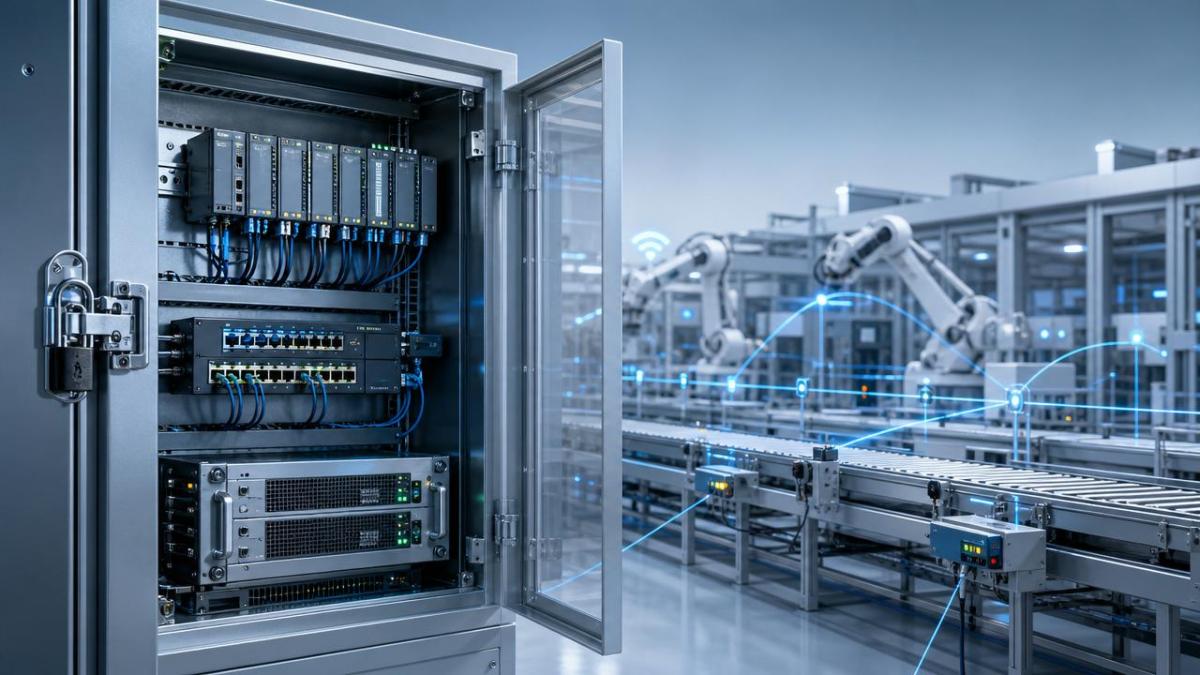
A scada system integrator connects control hardware, industrial software, networks, historians, alarms, and operator interfaces into a working supervisory environment.
The role is not limited to screen design or PLC communication setup.
A competent scada system integrator translates operational requirements into stable architecture, verified data models, maintainable logic, and secure access boundaries.
In integrated facilities, SCADA affects production speed, utility consumption, batch traceability, safety response, maintenance planning, and compliance evidence.
When integration quality declines, the damage spreads beyond the control room.
Small defects become hidden production losses, audit gaps, unstable reporting, and recurring engineering rework.
Measurable Signals That Replacement Is Becoming Necessary
The strongest replacement case appears when problems become measurable, repeated, and expensive.
A scada system integrator should be assessed with evidence from uptime records, change logs, cybersecurity reviews, and project delivery data.
One weak project may be recoverable.
A repeated pattern across sites, production lines, or upgrades indicates a structural supplier problem.
At that point, keeping the same scada system integrator may cost more than controlled transition.
Documentation and Knowledge Transfer Failures
Documentation quality is one of the clearest indicators of integration maturity.
A reliable scada system integrator provides updated architecture diagrams, tag lists, alarm philosophies, backup procedures, network maps, and change histories.
Poor documentation creates operational dependence on specific individuals.
That dependence becomes dangerous during expansions, emergency recovery, staff turnover, or vendor disputes.
Common documentation red flags
- Tag naming is inconsistent across PLC, HMI, historian, and reports.
- Backup files are outdated, incomplete, or stored without version control.
- Alarm priorities are undocumented or copied from default templates.
- Network diagrams do not match installed switches, gateways, or firewalls.
- Cause-and-effect logic is unavailable for critical process states.
If these issues persist after formal requests, the scada system integrator is no longer supporting lifecycle reliability.
Cybersecurity Discipline and Industrial Risk
Modern SCADA environments are no longer isolated islands.
They connect with MES, ERP, cloud analytics, remote support tools, edge gateways, and multi-site reporting platforms.
A scada system integrator must understand industrial cybersecurity beyond basic password settings.
Minimum competence includes network segmentation, least-privilege access, patch assessment, secure remote access, asset inventory, and recovery planning.
Replacement becomes justified when cybersecurity is treated as an optional add-on.
High-risk signs include shared accounts, unmanaged VPNs, open engineering workstations, unsupported operating systems, and missing offline backups.
The scada system integrator should also align practices with IEC 62443 principles where relevant.
Even without formal certification, the engineering logic should be visible, testable, and documented.
Project Delivery Patterns That Reveal Technical Limits
Schedule delays alone do not prove incompetence.
Industrial projects face site constraints, legacy systems, and changing production requirements.
However, a weak scada system integrator repeatedly fails at scope control, FAT readiness, commissioning planning, and issue closure.
Frequent surprises near startup often indicate poor front-end engineering.
Examples include untested communication drivers, missing tag validation, incomplete alarm rationalization, and insufficient operator training.
A mature scada system integrator uses structured project gates.
Requirements are frozen, assumptions are logged, test cases are prepared, and acceptance criteria are agreed before site pressure begins.
Misalignment With Production KPIs
SCADA is not valuable because screens look modern.
It is valuable when operational data supports faster response, higher throughput, lower waste, and better compliance.
A scada system integrator should understand how automation choices affect measurable business outcomes.
Key indicators include OEE visibility, downtime classification, batch reporting, energy monitoring, alarm frequency, and maintenance event capture.
Replacement should be considered when the scada system integrator delivers technical functions without operational usefulness.
For example, a historian may collect millions of tags while still failing to explain yield loss.
An alarm system may show every event while hiding the few alarms that actually require action.
Engineering truth lies in traceable outcomes, not interface quantity.
Typical Scenarios Where Replacement Is Justified
Replacement is rarely a purely emotional decision.
It is usually triggered by a gap between current integration capability and system criticality.
In these cases, the scada system integrator should not be judged only by responsiveness.
Fast reaction matters, but permanent correction matters more.
Practical Evaluation Before Making a Change
Replacing a scada system integrator introduces transition risk.
The decision should begin with a structured technical review, not an abrupt vendor swap.
- Audit architecture, backups, licenses, servers, network segmentation, and remote access paths.
- Review incident history and identify repeated failure modes.
- Check whether current documentation supports independent maintenance.
- Compare delivered functions against production KPIs and compliance needs.
- Request a corrective action plan with dates, evidence, and accountable owners.
If the current scada system integrator cannot respond with verifiable engineering evidence, replacement becomes a rational control measure.
The new selection process should test technical depth early.
Strong candidates explain trade-offs, ask process-specific questions, and challenge vague requirements before proposing tools.
Transition Controls That Reduce Replacement Risk
A poorly managed transition can create the same damage it was meant to solve.
Before replacing a scada system integrator, secure the operational baseline.
- Freeze nonessential changes during the assessment period.
- Create verified backups for PLC, SCADA, historian, and database assets.
- Confirm license ownership, source file access, and administrator credentials.
- Map dependencies between control logic, reporting tools, and external systems.
- Define rollback procedures for every high-risk modification.
The incoming scada system integrator should first stabilize knowledge, then improve architecture.
Immediate redesign without verified understanding often introduces avoidable downtime.
Evidence-Based Next Step
A scada system integrator should be replaced when measurable risk exceeds the value of continuity.
The clearest evidence includes recurring downtime, missing documentation, weak cybersecurity, poor project control, and limited KPI alignment.
The most practical next step is an independent SCADA health audit.
That audit should produce a ranked defect list, risk map, recovery plan, and integration capability score.
With those facts, replacement becomes an engineering decision rather than a commercial argument.
TechStat Vanguard supports this mindset: parameters do not lie, and tolerances dictate success.
When the evidence shows that a scada system integrator no longer protects the system, controlled replacement is not disruption.
It is a necessary step toward operational truth, resilient automation, and scalable industrial performance.
Search News
Hot Articles
- Carbon Fiber StructuresHow to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsJul 11, 2026
- Machine VisionXiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsMar 30, 2026
- Cobots & ArmsShanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsMar 30, 2026
Popular Tags
Recommended News
 Jul 11, 2026How to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsAerospace carbon fiber assemblies: learn how to specify laminate design, load data, joining methods, and inspection controls for lighter, reliable load-bearing aerospace parts.Elena Rostova (UAV Systems Researcher)
 Mar 30, 2026Xiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsXiaomi & Alibaba DAMO Academy's open-source robotics models lower algorithm barriers for global SMEs. Boost efficiency in manufacturing, logistics & smart retail with ROS 2 compatible solutions.TSV Data Lab
 Mar 30, 2026Shanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsShanxi 'AI+' Conference highlights embodied intelligence with Tesla, Ubtech & Jiantao showcasing multimodal robotics. 40+ global buyers validated tech on-site, creating new B2B channels for industrial automation & AI solutions.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Zhongguancun Unveils 6G Integrated Sensing-Computing-Intelligence Platform to Empower Embodied Robots for Global Industrial ApplicationsZhongguancun's new 6G platform revolutionizes industrial robotics with <10ms latency, empowering global automotive, logistics & port automation. Discover how this tech boosts China's smart manufacturing exports.TSV Data Lab
 Mar 30, 2026Mech-Mind Tianjin Embodied Intelligence R&D and Production Base Goes Live, Cutting Delivery Time by 20%–30% for Global Customized AMR+Vision SolutionsMech-Mind's Tianjin AMR+Vision production base cuts delivery time by 20%-30% for欧美 & Latin American markets. Discover how this PLd-certified facility accelerates customized robotics solutions for smart manufacturing and logistics.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Boao Forum Reveals 'Co-evolution of Big and Small Brains' Trend in Humanoid Robots, China's Embodied Intelligence Accelerates Adaptation to Overseas Manufacturing Service ScenariosDiscover how China's humanoid robots, featuring 'Co-evolution of Big and Small Brains,' are revolutionizing global manufacturing. Learn about Embodied Tian Gong 3.0's ISO compliance and overseas deployment at Boao Forum 2026.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026China Railway Industrial Secures Patent for Embodied Robotics in Material Handling, Boosting High-Precision Delivery Capabilities for Overseas Infrastructure and Manufacturing ProjectsChina Railway Industrial's new patent for embodied robotics in material handling boosts high-precision delivery for global infrastructure & manufacturing. Discover how this innovation enhances logistics accuracy in automotive, rail transit & EPC projects.Chen Wei (Automation Lead Engineer)
 Oct 15, 2026R&D Cost Reduction Services: How to Evaluate Fees, Savings, and ROIEvaluate R&D cost reduction services with confidence. Compare fees, verify savings, and calculate ROI without compromising performance. Discover how to choose a provider that delivers real value.Chen Wei (Automation Lead Engineer)
 Oct 14, 2026Drone Frame Composites: Carbon Fiber vs. Fiberglass for Weight and StiffnessExplore drone structural materials composites: compare carbon fiber and fiberglass for weight, stiffness, cost, and antenna compatibility. Find the right material for your drone frame.Elena Rostova (UAV Systems Researcher)
 Oct 13, 2026Smart Cameras vs. PC-Based Machine Vision: Which Fits High-Speed Inspection?This industrial product comparison for machine vision weighs smart cameras vs. PC-based systems on latency, throughput, and cost. Discover your best fit for high-speed inspection.TSV Data Lab
 Oct 12, 2026How to Verify RoHS Compliance in Industrial Sensing Systems Before DeploymentRoHS compliant sensing systems: learn how to verify materials, supplier declarations, testing, and configuration controls before industrial deployment.TSV Data Lab
 Oct 11, 2026How Procurement-Oriented Content Taxonomy Improves B2B Buying JourneysProcurement-oriented content taxonomy streamlines B2B buying journeys with clearer evidence, supplier comparisons, risk visibility, and faster approvals.TSV Data Lab
 Oct 10, 2026How to Select a Machine Performance Monitoring Platform for OEE and Downtime ReductionMachine performance monitoring platform selection guide: validate machine states, OEE data, downtime reasons, integrations, and scalability to reduce losses with confidence.TSV Data Lab
 Oct 08, 2026How to Machine Inconel 625 Blades Without Heat Cracks or Edge ChippingInconel 625 blade machining guide: prevent heat cracks, edge chipping, chatter, and work hardening with proven tooling, cooling, fixturing, and inspection strategies.Dr. Marcus Vance
 Oct 07, 2026How to Evaluate an HMI Panel Distributor for Industrial Automation ProjectsHMI panel distributor evaluation guide: verify technical compatibility, traceability, supply reliability, lifecycle support, and total cost for automation projects.Victor Lin (Chief Software Architect)
 Oct 06, 2026Navigation Fault Tolerance Standards for AMRs: What Safety Teams Must VerifyNavigation fault tolerance standards: learn what AMR safety teams must verify, from localization loss and sensor faults to stopping distance, safe restart, and site-specific validation.Chen Wei (Automation Lead Engineer)
 Oct 05, 2026Calculating Edge Computing Total Cost of Ownership Across Distributed SitesEdge computing ownership cost explained: calculate deployment, energy, connectivity, security, remote support, and refresh costs across distributed sites.TSV Data Lab
 Oct 04, 2026CAD/CAM Benchmarking in the GCC: What Manufacturers Should Ask a ConsultantCAD CAM benchmark consultant GCC guide: learn the key questions manufacturers should ask to validate post-processors, workflows, machine performance, and production risk.Victor Lin (Chief Software Architect)
 Oct 03, 2026Selecting Automotive Radar Sensor Modules for ADAS Range, Resolution, and IntegrationAutomotive radar sensor module selection guide for ADAS: compare range, resolution, field of view, latency, and integration to build safer, reliable vehicle systems.TSV Data Lab
 Oct 02, 2026How to Qualify Machined Parts Suppliers for Hard Tech ProgramsHard tech supply chain machined parts demand rigorous supplier qualification. Learn how to assess capability, traceability, quality controls, and delivery resilience.Dr. Marcus Vance
 Oct 01, 2026How to Select an Outdoor Security Radar Sensor for Perimeter Detection?Outdoor security radar sensor selection guide: compare range, accuracy, false-alarm control, integration, and field testing for reliable perimeter detection.TSV Data Lab
 Sep 30, 2026How to Evaluate Solid-State LiDAR Hardware for Outdoor Autonomous VehiclesSolid state LiDAR hardware evaluation guide for outdoor autonomous vehicles—compare range, point-cloud quality, environmental resilience, integration, and safety.TSV Data Lab
 Sep 29, 2026ISO 9283 Repeatability: How to Evaluate Cobot Positioning PerformanceISO 9283 cobot repeatability explained: learn how payload, reach, approach direction, and test conditions affect positioning performance and cell capability.Chen Wei (Automation Lead Engineer)
 Oct 14, 2026How tight can micro machining aerospace tolerances be in production?Micro machining aerospace tolerances can reach low-micron levels in production. Learn what controls repeatability, inspection confidence, and flight-critical quality.Dr. Marcus Vance























