How to Choose PLCs for Chemical Plants: Safety, Redundancy, and I/O Factors
Publication Date
author
How to Choose PLCs for Chemical Plants: Safety, Redundancy, and I/O Factors
Choosing PLCs for chemical plants is not just about control logic. It is a risk-management decision that sits right between process safety, uptime, maintenance reality, and long asset life. In a batch reactor area, a poor I/O decision can become a nuisance shutdown. In a solvent handling unit or chlorination section, the same mistake can become a serious incident. For technical evaluators comparing PLCs for chemical plants, the useful question is not “Which brand is best?” It is “Which platform still behaves predictably when instruments drift, a network segment drops, a power supply fails, and maintenance has to replace a card at 2 a.m. without guessing?”
That changes the checklist. You are not buying a controller in isolation. You are judging an architecture: safety integrity, hazardous-area fit, redundancy options, diagnostics depth, spare parts practicality, and whether the I/O strategy matches the real process rather than a clean drawing in a proposal deck.
Start With the Process Hazard, Not the PLC Catalog
A common selection error is to shortlist platforms before the process risk picture is fully clear. In chemical plants, that usually backfires. The first pass should be built around:
- Whether the unit is continuous, batch, or hybrid.
- What shutdowns are expensive versus what shutdowns are mandatory.
- Which loops are merely operational and which are tied to safety functions.
- Where hazardous areas exist and how field devices are installed there.
- What the plant can tolerate during maintenance: hitless switchover, brief interruption, or full outage.
If the project has a formal hazard analysis, LOPA, or SIS/SIL basis, the PLC decision has to follow that work instead of trying to replace it. Do not let general-purpose control and safety requirements blur together. In many chemical facilities, the most expensive mistakes come from treating a process control PLC as if it can cover all protective functions by configuration alone. Whether a separate safety PLC or integrated safety architecture is appropriate depends on the application and lifecycle requirements, but the distinction has to be explicit.
Check the Safety Architecture Before You Compare Features
For chemical environments, “safety capable” is too vague to be useful. The questions that matter are plainer:
- Does the platform support the required safety lifecycle documentation?
- Can it be deployed in the target architecture without awkward third-party workarounds?
- How are safety I/O, proof testing, bypass handling, and diagnostics managed?
- What is the failure behavior of outputs on loss of communication, module fault, or processor switchover?
For standards, stay grounded. Functional safety discussions usually point toward IEC 61511 at the process-industry system level and IEC 61508 at the underlying electrical/electronic/programmable safety system level. Hazardous locations may bring in ATEX, IECEx, NEC, or local code requirements depending on geography. Those are not box-ticking add-ons. They affect hardware selection, panel design, wiring method, and maintenance practice.
If a vendor cannot clearly map its PLC and safety components to your required compliance path, treat that as an early warning. In practice, documentation quality is often a better predictor of project friction than glossy feature lists.
Redundancy Is Not a Badge. It Has to Match the Failure You Care About.
People ask for redundancy as if it were one thing. It is not. In PLC selection for chemical plants, you need to separate at least four layers:
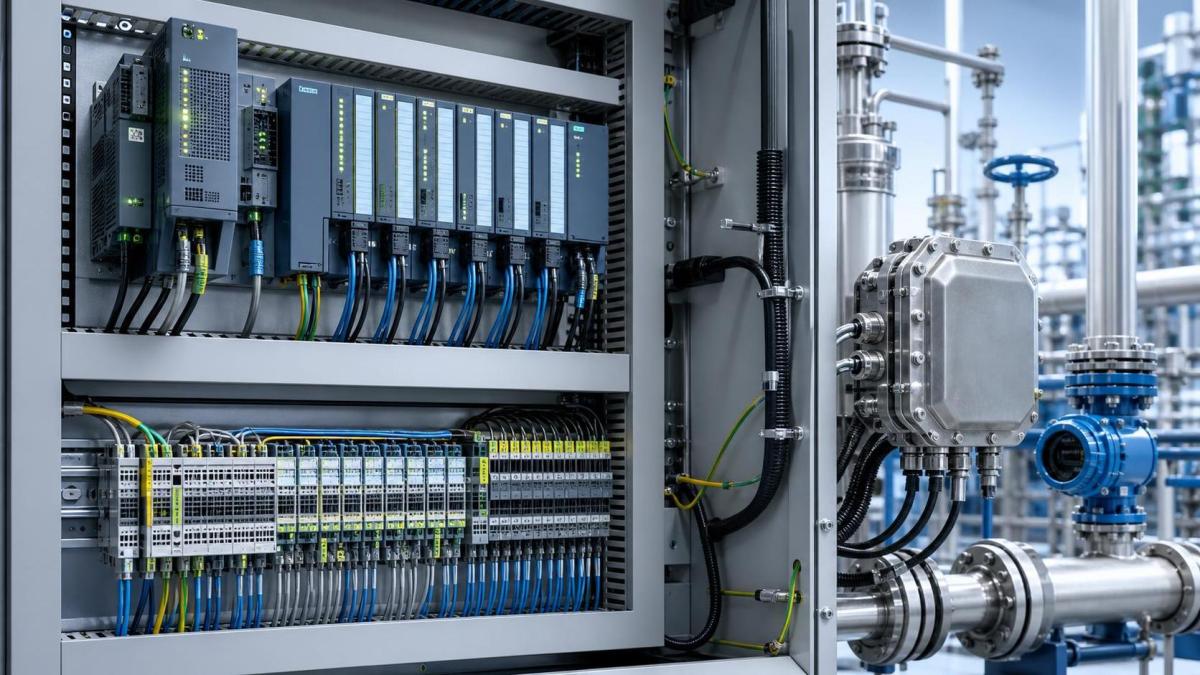
This is where many specifications get sloppy. A redundant CPU does not solve a single nonredundant remote I/O head in a corrosive area. A ring network does not help if the instrument power architecture remains single-point fragile. Ask the plant team what failures they have actually seen over the last five years. Module faults? Network storms? Condensation in marshalling cabinets? Brownouts? That history usually tells you where redundancy earns its keep.
Also check whether redundancy adds operational constraints. Some platforms limit online changes, firmware management, or mixed module use when redundant mode is enabled. Those details matter more during turnarounds than during factory demos.
Do Not Underestimate I/O Strategy
A lot of chemical plant PLC projects look acceptable at controller level and then become messy at the I/O layer. That is because field reality is harsh: long cable runs, analog noise, intrinsically safe barriers, valve feedback that is less clean than the P&ID suggests, and a maintenance team that needs channel-level diagnostics fast.
When evaluating I/O, I would not stop at total point count. Check these items directly:
- Analog input quality for 4-20 mA and other required signal types, including isolation and noise immunity.
- Support for HART pass-through or asset information access if your maintenance workflow depends on it.
- Channel-level diagnostics rather than module-only fault visibility.
- Remote I/O suitability for ambient temperature, vibration, ingress protection, and corrosive atmosphere exposure.
- Whether intrinsic safety or explosion protection requirements push you toward specific remote I/O families or barriers.
- Spare capacity, both physical and electrical, because chemical plants almost always add instruments later.
One practical rule: leave room for ugly signals. A beautifully sized I/O list with no spare analog channels and no cabinet margin tends to age badly within a year of startup.
Hazardous Area Fit Is a Real Selection Gate
For PLCs for chemical plants, hazardous-area compatibility is often where shortlists get cut. The controller may stay in a safe area, but the architecture still has to respect how instruments, remote I/O, barriers, and enclosures are deployed. Zone/Class/Division interpretation varies by jurisdiction and site standard, so confirm the exact basis early. If your project spans regions, do not assume a design accepted in one market transfers cleanly to another without review.
This is also where “integrated” solutions can hide cost. A platform may look simple on paper, then require additional interface hardware, certified barriers, or cabinet redesign to satisfy the actual installation method. Ask for a realistic bill of architecture, not just a CPU quote.
Look Hard at Lifecycle and Maintainability
Technical evaluators sometimes focus so tightly on startup capability that they miss the ten-year maintenance burden. In chemical plants, that is backwards. These systems are expected to stay supportable through expansion, partial migration, and staff turnover.
What I would verify before approving a platform:
- Firmware and software version management. Can the site realistically control revisions across redundant nodes, engineering stations, and remote I/O?
- Availability of local support and trained integrators. A strong platform with weak regional support becomes expensive fast.
- Obsolescence roadmap. Ask directly what is current, what is mature, and what is already on the migration path.
- Online change capability and recovery procedures. Maintenance teams care about this more than brochure writers do.
- Spare part stocking logic. Do not assume corporate procurement can source critical modules quickly during a shutdown window.
This is one area where TSV’s general philosophy applies cleanly: parameters matter, but supportability is also a parameter. If you cannot define replacement lead times, revision control method, and fault recovery workflow, the evaluation is incomplete even if the controller benchmark looks strong.
Cybersecurity and Segmentation Belong in the Selection Phase
Chemical plants increasingly sit inside broader OT and enterprise connectivity plans. That does not mean every PLC must be internet-aware. It does mean the platform should fit a sensible security model: user roles, change auditing, network segmentation, secure remote access approach, and controlled integration with SCADA, historians, MES, or edge systems. IEC 62443 may be relevant depending on the organization’s policy and project scope, but the exact compliance expectation should be confirmed with the site cybersecurity team rather than assumed.
A small but useful test: ask the vendor or integrator to explain how they handle backup restoration, engineering workstation hardening, and remote troubleshooting without hand-waving. If the answer is vague, the future incident report will probably be vague too.
Vendor Comparisons Should Be Scenario-Based
Side-by-side datasheet comparison is necessary, but it is rarely enough for choosing PLCs for chemical plants. Build a few operating scenarios and make each vendor walk through them:
- Loss of one CPU during normal production.
- Failure of a remote I/O node in a hazardous process area.
- Analog transmitter bad value during a critical batch step.
- Network interruption between controller and HMI or historian.
- Hot replacement of a failed module during a narrow maintenance window.
You learn more from those walkthroughs than from feature matrices. The goal is to expose hidden dependencies, licensing traps, restart behavior, and operator impact. It also shows whether the vendor understands process operations or only product positioning.
A Short List of Mistakes Worth Avoiding
A few issues show up often enough to be worth calling out plainly.
- Specifying redundancy everywhere without ranking critical loops. That inflates cost and complexity without reducing the right risk.
- Treating safety PLC functions as interchangeable with standard process control logic.
- Ignoring diagnostics depth at channel level, then discovering troubleshooting is too slow during commissioning.
- Underestimating future I/O growth, especially analog and specialty signals.
- Approving a platform before confirming local service capability, spare part path, and lifecycle status.
None of these are exotic errors. They are ordinary evaluation shortcuts, and they usually surface late, when changing course is expensive.
What a Good Final Decision Usually Looks Like
A solid decision on PLCs for chemical plants is usually easy to explain in one page. The chosen platform fits the plant’s safety basis, supports the required redundancy at the layers that actually matter, gives maintainable I/O diagnostics, respects hazardous-area constraints, and comes with a believable long-term support path. If you need three pages of exceptions and workarounds to justify the choice, the architecture is probably fighting the plant.
Before sign-off, I would want one final review with operations, process engineering, instrumentation, maintenance, and OT security in the same room. Not to admire features. To ask a blunt question: when this system is stressed, failed over, modified, and repaired in real plant conditions, do we still trust its behavior? That is the standard worth using.
Search News
Hot Articles
- Carbon Fiber StructuresHow to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsJul 11, 2026
- Machine VisionXiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsMar 30, 2026
- Cobots & ArmsShanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsMar 30, 2026
Popular Tags
Recommended News
 Jul 11, 2026How to Specify Aerospace Carbon Fiber Assemblies for Lightweight, Load-Bearing PartsAerospace carbon fiber assemblies: learn how to specify laminate design, load data, joining methods, and inspection controls for lighter, reliable load-bearing aerospace parts.Elena Rostova (UAV Systems Researcher)
 Mar 30, 2026Xiaomi, Alibaba DAMO Academy Drive Open-Source Robotics Model Ecosystem, Lowering Algorithm Development Barriers for Overseas SMEs Adopting Chinese Robotics SolutionsXiaomi & Alibaba DAMO Academy's open-source robotics models lower algorithm barriers for global SMEs. Boost efficiency in manufacturing, logistics & smart retail with ROS 2 compatible solutions.TSV Data Lab
 Mar 30, 2026Shanxi 'AI+' Conference Showcases Embodied Intelligence with Multinational Buyer Engagement: Key Industry ImplicationsShanxi 'AI+' Conference highlights embodied intelligence with Tesla, Ubtech & Jiantao showcasing multimodal robotics. 40+ global buyers validated tech on-site, creating new B2B channels for industrial automation & AI solutions.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Zhongguancun Unveils 6G Integrated Sensing-Computing-Intelligence Platform to Empower Embodied Robots for Global Industrial ApplicationsZhongguancun's new 6G platform revolutionizes industrial robotics with <10ms latency, empowering global automotive, logistics & port automation. Discover how this tech boosts China's smart manufacturing exports.TSV Data Lab
 Mar 30, 2026Mech-Mind Tianjin Embodied Intelligence R&D and Production Base Goes Live, Cutting Delivery Time by 20%–30% for Global Customized AMR+Vision SolutionsMech-Mind's Tianjin AMR+Vision production base cuts delivery time by 20%-30% for欧美 & Latin American markets. Discover how this PLd-certified facility accelerates customized robotics solutions for smart manufacturing and logistics.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026Boao Forum Reveals 'Co-evolution of Big and Small Brains' Trend in Humanoid Robots, China's Embodied Intelligence Accelerates Adaptation to Overseas Manufacturing Service ScenariosDiscover how China's humanoid robots, featuring 'Co-evolution of Big and Small Brains,' are revolutionizing global manufacturing. Learn about Embodied Tian Gong 3.0's ISO compliance and overseas deployment at Boao Forum 2026.Chen Wei (Automation Lead Engineer)
 Mar 30, 2026China Railway Industrial Secures Patent for Embodied Robotics in Material Handling, Boosting High-Precision Delivery Capabilities for Overseas Infrastructure and Manufacturing ProjectsChina Railway Industrial's new patent for embodied robotics in material handling boosts high-precision delivery for global infrastructure & manufacturing. Discover how this innovation enhances logistics accuracy in automotive, rail transit & EPC projects.Chen Wei (Automation Lead Engineer)
 Oct 23, 2026US Navy Raises Gecko Robotics Contract Ceiling to $300M for Robotic Fleet MaintenanceUS Navy raises Gecko Robotics’ contract ceiling to $300M for Pacific Fleet robotic inspections. Explore potential opportunities for maintenance suppliers and key procurement considerations.Chen Wei (Automation Lead Engineer)
 Oct 23, 2026Choosing Industrial Sensing Systems for Global Plants: Protocol CompatibilityCompare industrial sensing systems international buyers can trust. Explore protocol compatibility, reduce integration risks, and select proven configurations for reliable global plant deployments.TSV Data Lab
 Oct 22, 2026KUKA Showcases Physical AI and iiQKA.AI Vision at NVIDIA GTC BerlinExplore KUKA’s Physical AI showcase at NVIDIA GTC Berlin and discover how iiQKA.AI Vision aims to simplify robotic vision integration and improve 2D and 3D scene recognition.TSV Data Lab
 Oct 22, 2026Robotic Machining of Advanced Composites: What Tolerances Are Achievable?Explore advanced materials machining robotics: discover what drives achievable composite tolerances and how to validate accuracy before investing in your next machining system.Dr. Marcus Vance
 Oct 21, 2026China’s Industrial Robot Exports Near RMB 10 Billion in First Nine Months of 2026China’s industrial robot exports neared RMB 10 billion in January–September 2026, with value rising faster than volume. Explore the data and what it could mean for suppliers.Chen Wei (Automation Lead Engineer)
 Oct 21, 2026Low-Latency Industrial Data Processing: Pricing and Key Cost DriversExplore industrial data latency price drivers, from edge hardware to integration and support. Learn how to compare quotes, verify performance, and avoid unnecessary costs.TSV Data Lab
 Oct 20, 2026KUKA Launches iiQKA.AI Vision to Simplify Industrial Image ProcessingKUKA iiQKA.AI Vision simplifies industrial image processing with controller-based 2D and 3D vision. Explore drag-and-drop setup for vision-guided automation.TSV Data Lab
 Oct 20, 2026Smart Industrial Edge Devices: Key Criteria for Legacy PLC IntegrationChoose smart industrial edge devices for legacy PLC integration. Discover key criteria for compatibility, data quality, security, and reliable collection without disrupting control.TSV Data Lab
 Oct 19, 2026Choosing a Radar Sensor by Application: Range, Resolution, and Field of ViewSimplify radar sensor application based product selection. Compare range, resolution, and field of view to avoid blind spots and choose with confidence. Explore the guide.TSV Data Lab
 Oct 18, 2026Comparing Material Options for Procurement: Specs, Costs, and Supply RisksExplore procurement oriented technical content on material options, specs, costs, and supply risks. Compare alternatives to cut hidden expenses and make confident sourcing decisions.Dr. Marcus Vance
 Oct 17, 20265-Axis CNC Positioning Accuracy: How to Interpret ISO 230-2 Test ResultsAssess 5 axis CNC machining positioning accuracy with ISO 230-2. Learn to interpret repeatability, reversal error, and test conditions to compare suppliers and make confident acceptance decisions.Dr. Marcus Vance
 Oct 16, 2026Choosing a Rugged Edge AI Box Supplier: Thermal Tests and Lifecycle SupportChoose a rugged edge AI box supplier with proven thermal performance and reliable lifecycle support. Discover the tests and commitments to verify before you buy.TSV Data Lab
 Oct 15, 2026R&D Cost Reduction Services: How to Evaluate Fees, Savings, and ROIEvaluate R&D cost reduction services with confidence. Compare fees, verify savings, and calculate ROI without compromising performance. Discover how to choose a provider that delivers real value.Chen Wei (Automation Lead Engineer)
 Oct 23, 2026How Do You Evaluate Solid-State LiDAR Point Cloud Density?Evaluate solid-state LiDAR point cloud density using valid returns, angular spacing, and real-world coverage. Discover how to compare sensors and choose the right fit for your application.TSV Data Lab
 Oct 22, 2026How Do You Test AMR Navigation Accuracy in a Warehouse?Test AMR navigation accuracy in warehouses with practical methods for localization, path tracking, and docking. Learn to set tolerances and compare robots before deployment.Chen Wei (Automation Lead Engineer)
 Oct 21, 2026How Should You Balance Cobot Payload Against Reach?Explore cobot payload versus reach to choose the right robot. Learn how tooling, load limits, workspace, and cycle time affect performance—and avoid costly selection mistakes.Chen Wei (Automation Lead Engineer)
 Oct 20, 2026How Do You Measure Industrial IoT Gateway Latency Under Load?Measure industrial IoT gateway latency under load with reliable timestamps, realistic traffic, and tail-latency analysis. Discover how to expose bottlenecks and choose the right gateway.TSV Data Lab